WordPress released version 7.1.4 to fix a race condition in its update process that could enable code execution. The security notice describes fixes for supported branches. Exploitation attempts were reported soon after the release, but do not establish that every vulnerable site was compromised.
Administrators should identify their branch, install the applicable fix, and review changes made during the exposure period.
The issue that was fixed
The WordPress security advisory describes a synchronisation problem around the update process. Under certain conditions, the race could open a path to code execution. The official notice lists affected versions and fixes; sites should follow its update matrix instead of assuming one release applies to every branch.
WordPress 7.1.4 contains the main fix, with backports for maintained branches. If your host manages updates, confirm the version actually installed in its control panel.
Attempts are not confirmed compromise
SecurityWeek and The Hacker News report that attackers began attempting to exploit the flaw. Observed attempts show active exposure, but do not by themselves prove that a specific site was compromised.
After patching, review available logs, changed files, administrator accounts, and installed plugins. Investigate anomalies under your incident process and preserve relevant evidence.
Patch promptly
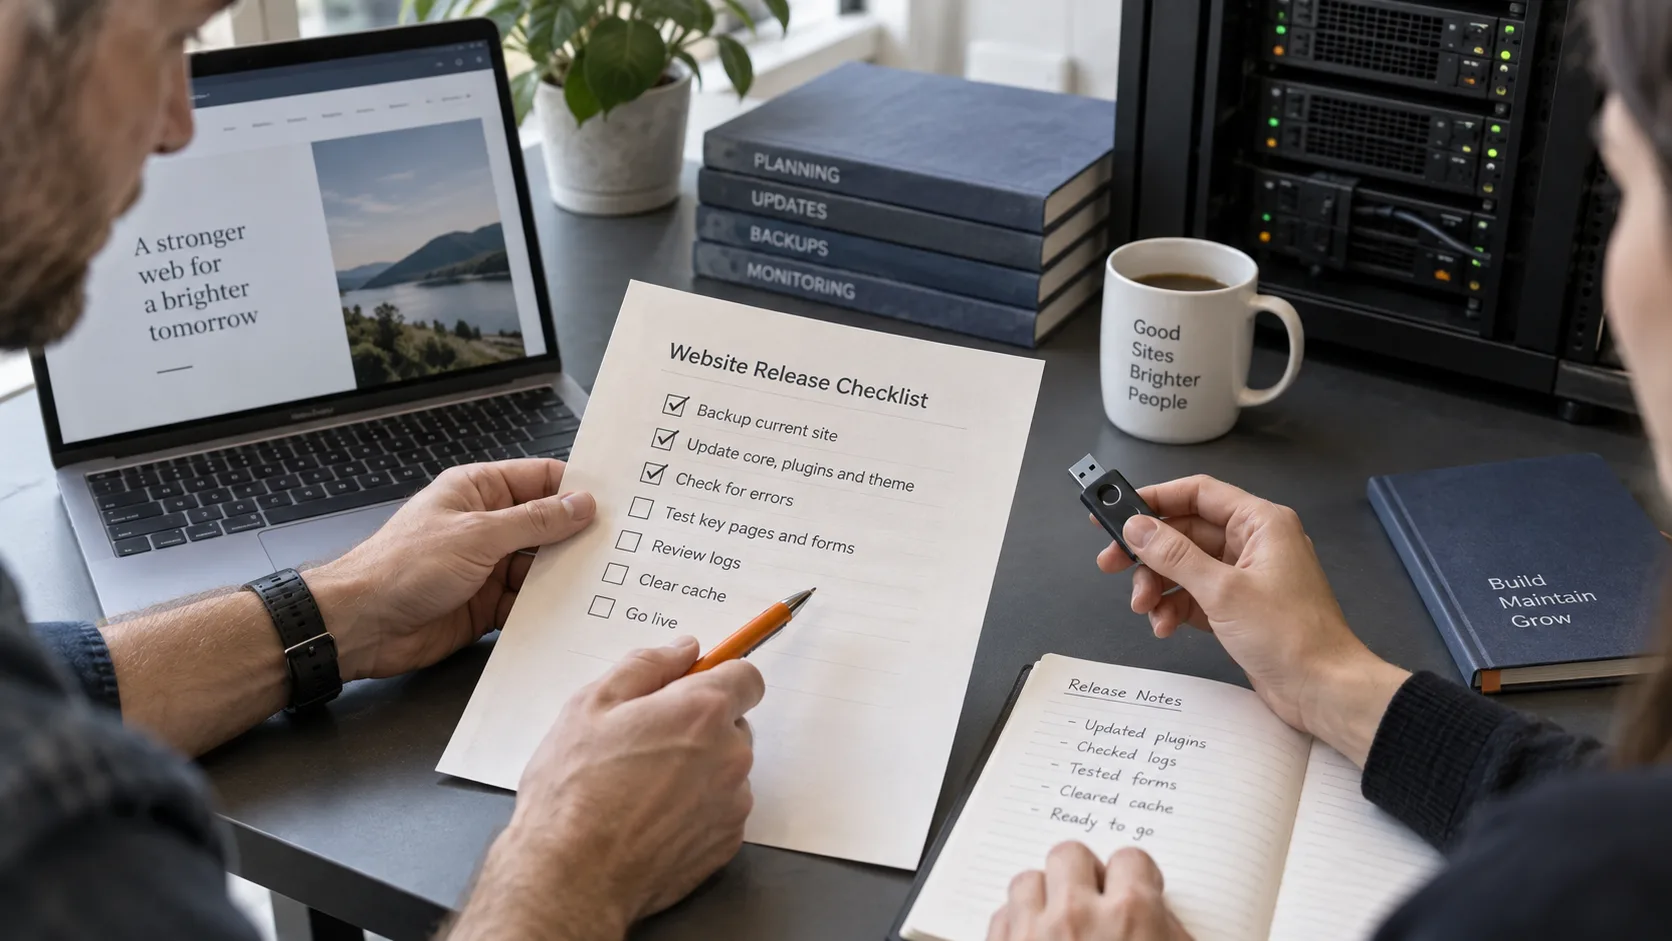
Identify the WordPress branch for each site, apply its fixed release, and confirm the update completed successfully. Follow your normal backup process before major maintenance and then check the site’s essential functions.
A core update does not replace review of plugins and themes. Keep those current through official sources too, and remove components that are no longer used.
Limit the impact of account compromise
Limit administrator accounts to people who need them and use unique passwords. Review new accounts and configuration changes after suspected exposure. If a credential may have been accessible from a compromised site, change it at the relevant service and revoke available sessions or tokens.
Soclyde’s connection
Soclyde lets teams keep the credentials they manage in an encrypted vault stored on their devices. It does not update WordPress or replace review of administrator accounts. See our guide to local versus cloud storage to organise your access.
What to remember
WordPress 7.1.4 and supported-branch fixes address an update race condition. Attempts have been reported, without evidence of universal compromise. Install the appropriate fix, confirm the version, and review site activity.